Post-Quantum Cryptography: How It Will Protect Data in the Future
Post-quantum cryptography helps protect sensitive data against future quantum computing threats. Explore how it works, key encryption methods, and why it matters for stronger digital security.
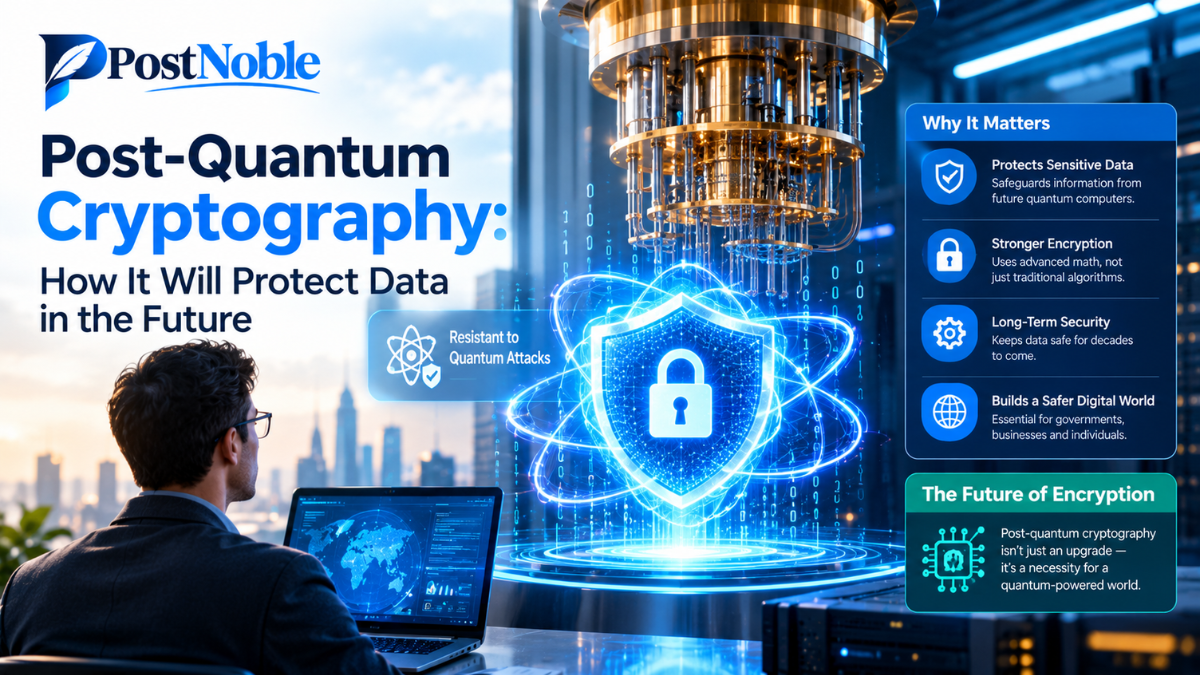
Technology is changing faster than ever, and the way we protect our digital information must change with it. Every day, people share personal details, make online payments, store business documents, and communicate through digital platforms. Behind these everyday activities, cryptography works quietly to keep sensitive information secure.
However, the development of powerful quantum computers could create new challenges for some of the encryption methods we use today. This is where post-quantum cryptography becomes important. It aims to protect digital information against attacks from both traditional computers and future quantum computers.
Although large-scale quantum computers capable of breaking widely used public-key cryptography are not yet a practical reality, preparing for this possibility is already an important part of cybersecurity planning.
In this article, PostNoble explores how post-quantum cryptography works, the methods being developed, and why this technology could play a major role in protecting data in the future.
What Is Post-Quantum Cryptography?
Post-quantum cryptography (PQC) refers to cryptographic algorithms designed to remain secure against attacks from classical computers and quantum computers.
Today, many digital security systems depend on mathematical problems that are extremely difficult for conventional computers to solve. For example, widely used public-key systems such as RSA and elliptic-curve cryptography rely on problems that sufficiently powerful quantum computers could potentially solve much more efficiently.
If that happens, some existing methods used to secure online communications, digital identities, and sensitive records could become vulnerable.
Post-quantum cryptography takes a different approach. It uses mathematical techniques believed to resist attacks from quantum computers while remaining practical for use on ordinary devices and networks.
Importantly, post-quantum cryptography is not the same as quantum cryptography. PQC uses algorithms that run on conventional computers, whereas quantum cryptography relies on principles of quantum physics.
Why Do We Need Post-Quantum Cryptography?
You might wonder why businesses should prepare for quantum computing threats when such computers cannot currently break all modern encryption in practical, real-world conditions.
One important reason is the “harvest now, decrypt later” risk. An attacker could collect encrypted information today and store it, hoping to decrypt it when more capable quantum computers become available.
This is particularly concerning for information that must remain confidential for many years, including financial records, government communications, medical information, and intellectual property.
There is also the challenge of updating existing technology. Large organizations may operate thousands of applications, servers, devices, and connected systems. Replacing their cryptographic infrastructure can take considerable time.
Preparing early allows organizations to identify vulnerable systems, test suitable alternatives, and reduce the risk of a rushed transition later.
How Post-Quantum Cryptography Works
Understanding how post-quantum cryptography works becomes easier when we look at how digital security operates in everyday situations.
Imagine sending a confidential document to a colleague. Before the document is transmitted, your system needs a secure way to establish encryption keys. The recipient also needs a reliable way to confirm the sender's identity and verify that the document has not been altered.
Post-quantum cryptography introduces algorithms designed to perform these security functions while resisting known quantum-computing threats.
Many proposed and standardized PQC algorithms rely on mathematical problems involving structures such as lattices or on the security properties of cryptographic hash functions. These problems are believed to remain difficult for both conventional and quantum computers, although security research continues.
The National Institute of Standards and Technology (NIST) published three major post-quantum cryptography standards in August 2024:
- ML-KEM: Helps two parties establish a shared secret key over a public communication channel.
- ML-DSA: Supports digital signatures that help verify the authenticity and integrity of information.
- SLH-DSA: Provides another digital signature approach based on cryptographic hash functions.
These standards give developers and organizations practical starting points for upgrading their security systems. Their security depends on correct implementation, appropriate parameter selection, and continued cryptographic evaluation.
5 Important Post-Quantum Encryption Methods and Technologies
Post-quantum security is not built around one universal algorithm. Different methods serve different purposes, from establishing secret keys to verifying digital signatures.
1. Lattice-Based Cryptography
Lattice-based cryptography is one of the most prominent approaches in modern post-quantum security.
It uses mathematical structures called lattices and problems that are believed to be difficult to solve efficiently, even with a sufficiently capable quantum computer.
For example, ML-KEM uses a module-lattice-based design to help establish shared secret keys. Those keys can then be used with symmetric encryption to protect messages and files.
This approach is important because secure key establishment is a fundamental part of online banking, private messaging, and many other digital services.
2. Hash-Based Cryptography
Hash-based cryptography uses cryptographic hash functions to support security operations such as digital signatures.
A hash function converts data into a fixed-length output. Secure hash functions are designed to make it computationally difficult to recover the original information or find certain matching inputs.
SLH-DSA is a standardized hash-based digital signature scheme designed to resist quantum attacks.
This method offers a different mathematical foundation from lattice-based cryptography, making it a valuable option for systems that need alternative security approaches.
3. Code-Based Cryptography
Code-based cryptography relies on mathematical problems related to error-correcting codes. These codes are commonly used in communications and data storage to detect or correct errors.
Some code-based cryptographic systems are designed to allow secure key establishment without depending on the mathematical problems used by RSA or elliptic-curve cryptography.
NIST selected the code-based HQC algorithm for standardization in 2025 as an additional key-establishment option. It is intended to complement the lattice-based ML-KEM standard.
Code-based approaches are significant because maintaining diversity in cryptographic designs can help strengthen long-term security planning.
4. Post-Quantum Digital Signatures
Encryption is only one part of cybersecurity. Organizations also need to verify that messages, software updates, and digital documents genuinely come from trusted sources.
Post-quantum digital signatures help address this need. They allow recipients to verify a signature and detect unauthorized changes to signed information.
ML-DSA and SLH-DSA are two standardized options designed for this purpose.
In the future, these technologies could help protect software distribution, digital certificates, online transactions, and systems that depend on trusted identities.
5. Hybrid Cryptographic Systems
Hybrid cryptographic systems combine a traditional cryptographic method with a post-quantum method during a transition period.
For example, a communication protocol may combine an established key-exchange method with a post-quantum key-establishment mechanism. Depending on the design, the system can retain security benefits from both approaches.
Hybrid deployment can help organizations move gradually toward quantum-resistant security while supporting compatibility with existing infrastructure.
However, a hybrid system must be designed and implemented carefully. Combining algorithms does not automatically make a system secure.
Where Will Post-Quantum Cryptography Be Used?
Post-quantum cryptography could support security across many industries as organizations modernize their digital infrastructure.
- Banking and finance: Protecting sensitive communications, customer information, and digital transactions.
- Healthcare: Helping safeguard patient records and confidential medical information that may need long-term protection.
- Cloud computing: Strengthening key establishment and secure connections between applications, servers, and cloud services.
- Government systems: Supporting the protection of sensitive communications and important digital records.
- IoT and connected devices: Preparing smart devices and industrial systems for future cryptographic requirements.
The actual implementation will depend on each system's security requirements, performance limits, and compatibility needs.
Challenges in Adopting Post-Quantum Cryptography
Despite its potential, adopting post-quantum cryptography will require careful planning.
Some post-quantum algorithms use larger keys, signatures, or exchanged messages than their traditional counterparts. These differences can affect network performance, storage requirements, and devices with limited processing power.
Organizations must also identify where older cryptographic algorithms are being used. Encryption may be built into software libraries, security certificates, hardware, and third-party services, making a complete inventory essential.
Another challenge is implementation quality. Even a well-designed algorithm can fail to protect information if developers use it incorrectly, mishandle secret keys, or overlook other security weaknesses.
For these reasons, organizations should follow established standards, test updates before deployment, and maintain a clear migration plan.
How Businesses Can Prepare for the Quantum Future
Businesses do not need to wait for a major quantum breakthrough before taking practical steps.
They can begin by identifying systems that depend on vulnerable public-key cryptography, prioritizing information that requires long-term confidentiality, and checking whether their technology providers support recognized post-quantum standards.
Security teams should also monitor developments from trusted standards organizations and plan updates for software, infrastructure, and connected devices.
The goal is not simply to replace one algorithm with another. It is to build a flexible security environment that can adapt as cryptographic standards and threats evolve.
Conclusion
Post-quantum cryptography is becoming an important part of the future of digital security. As quantum computing advances, existing cryptographic systems may face new risks, making it essential to prepare reliable alternatives.
From lattice-based algorithms and hash-based signatures to hybrid security systems, the available approaches offer different ways to strengthen digital protection. However, successful adoption will require thoughtful planning, careful implementation, and continued security evaluation.
For businesses and individuals alike, understanding these developments is a valuable first step toward protecting sensitive information in the years ahead.
At PostNoble, we believe that staying informed about emerging technologies helps readers make smarter decisions about digital security. Preparing for the quantum era today can help build a more resilient and trustworthy digital future tomorrow.